
Deleto
Browser-based credential sharing with AES-256-GCM, self-destructing links, and zero-knowledge handling.
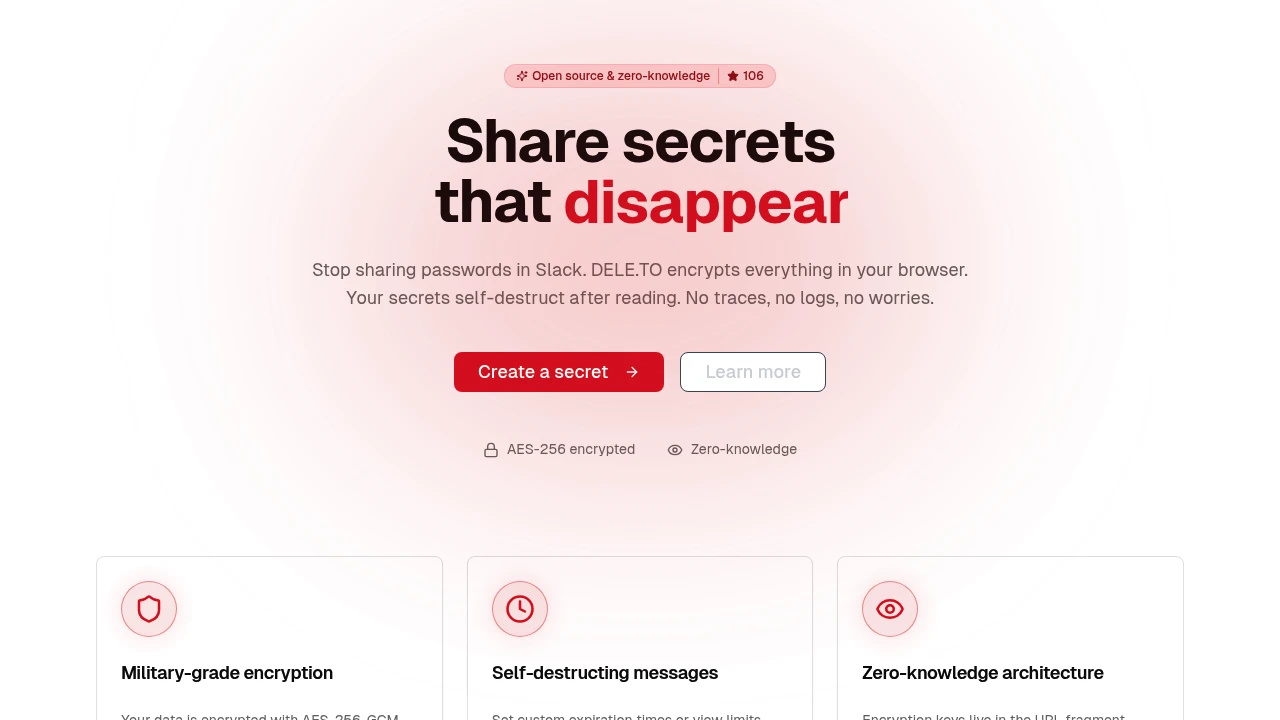
DELE.TO is a secure secret-sharing tool for sending passwords, API keys, and other sensitive text without exposing the plaintext to the service. It encrypts secrets directly in the browser before they are sent, then creates a link that can automatically expire after a defined period or number of views.
It is designed for people who need to share sensitive information quickly without putting plaintext secrets into chat, email, or other everyday communication channels. Basic sharing requires no signup, while the zero-knowledge architecture keeps encryption keys in the URL fragment rather than on the server.
Key Features
Client-Side Encryption
Encrypt sensitive information directly in the browser before it leaves your device.
- AES-256-GCM encryption
- Encryption happens in the browser
- Plaintext secrets are not exposed to the service
- Encryption keys remain in the URL fragment
Self-Destructing Links
Create links that automatically stop working after a defined condition is reached.
- Time-based expiration
- View-based expiration
- Secrets disappear after being read
- Useful for temporary credential sharing
No Signup Required
Share sensitive information without creating an account for basic use.
- No account required
- Designed for quick one-off sharing
- Simple link-based workflow
Privacy-Focused Design
DELE.TO states that it does not retain shared secret data or track users through IP logging.
- No IP logging
- No user tracking
- Zero-knowledge architecture
- Sensitive content is encrypted before being transmitted
Open Source
The project's source code is publicly available for inspection.
- Open-source implementation
- Available for security review
- Code available on GitHub
- Transparent encryption workflow
Command-Line Interface
Use DELE.TO directly from terminal workflows when handling sensitive output.
The CLI can work with:
- Piped command output
- Files
- Environment variables
.envfiles- Kubernetes output
- Other shell-based workflows
Browser Extension
Create secure, time-limited sharing links directly from selected text in your browser.
- Select sensitive text
- Create an encrypted link
- Set an expiration
- Share without leaving the current webpage
Built For Secure Secret Sharing
DELE.TO is designed for people who need to transfer sensitive information temporarily without placing plaintext credentials into normal messaging channels.
It is particularly suited to:
- Developers sharing API keys and credentials
- DevOps teams handling deployment secrets
- Security-conscious users sharing sensitive text
- IT teams transferring temporary credentials
- Technical teams working with shell and Kubernetes workflows
Common Use Cases
Sharing Passwords
Send a password through an expiring link instead of putting the plaintext credential directly into an email or chat message.
Sharing API Keys
Create a temporary link for transferring API keys while limiting how long the secret remains accessible.
DevOps Workflows
Use the CLI to encrypt sensitive terminal output, environment variables, .env files, or Kubernetes-related information.
Quick Credential Handoffs
Share sensitive information with a colleague without requiring either person to create an account.
Browser-Based Sharing
Use the browser extension to turn selected text into a temporary encrypted link directly from a webpage.
Zero-Knowledge Secret Sharing
DELE.TO's encryption model is built around keeping the plaintext secret away from the server.
The browser encrypts the data before transmission, while the encryption key is kept in the URL fragment. This means the service can handle the encrypted payload without needing access to the unencrypted secret.
Expiring Secret Links
Instead of sending a permanent message containing sensitive information, DELE.TO creates a temporary link that can be configured around time or view limits.
That makes the link suitable for situations where a credential only needs to be accessible briefly or should disappear after it has been retrieved.
CLI & Developer Workflows
The command-line interface makes DELE.TO useful beyond browser-based sharing. Developers can integrate secret sharing into existing shell workflows and encrypt information coming from commands, files, environment variables, or infrastructure tools.
This makes the tool particularly relevant when sensitive information already exists in a terminal-based workflow.
Cloud Option For Teams
DELE.TO also offers a dedicated cloud option for teams that want an isolated deployment.
The team-focused option provides:
- Dedicated deployment
- Custom domain
- Managed hosting
- An isolated environment for organizational use
Why It Matters
Sending passwords, API keys, and other secrets through ordinary communication tools can leave sensitive information sitting in message histories or email threads. DELE.TO provides a temporary link-based workflow where the secret is encrypted before it reaches the service.
The combination of client-side encryption, expiring links, no-signup sharing, open-source code, CLI support, and browser integration makes it useful for temporary sharing of sensitive information without exposing plaintext secrets to the service.
Share Sensitive Information With DELE.TO
Encrypt passwords, API keys, and other sensitive text in your browser, create an expiring link, and share it without putting the plaintext secret into chat or email.


